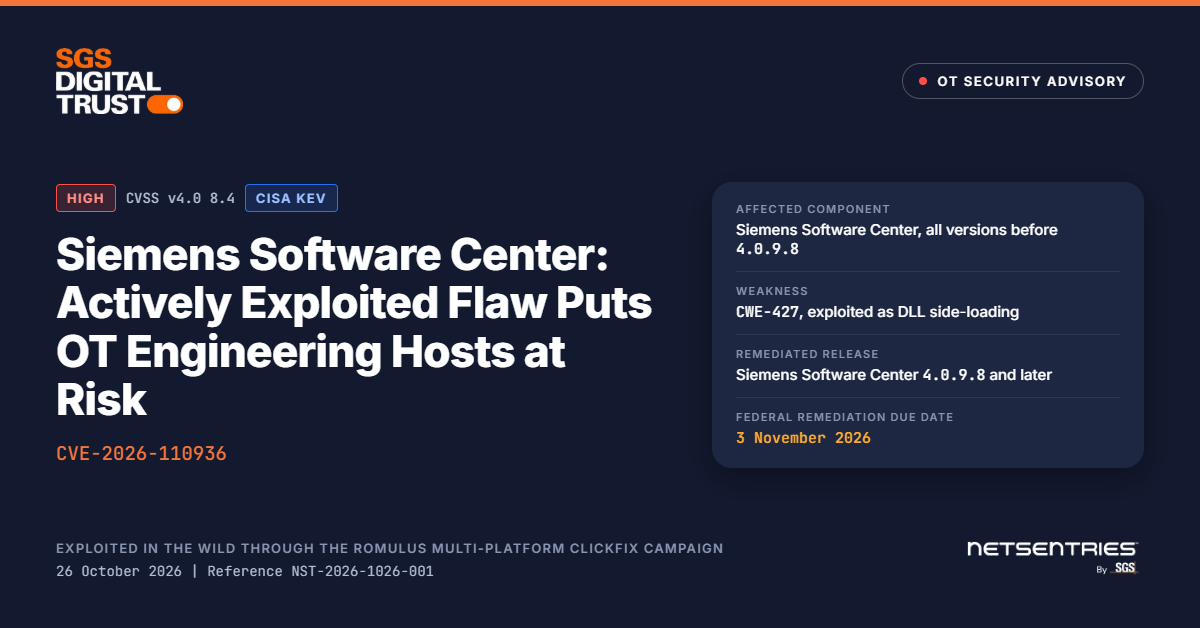
Siemens Software Center: Actively Exploited Flaw Puts OT Engineering Hosts at Risk
🚨 OT Security Advisory: Actively Exploited Siemens Software Center Vulnerability
CVE-2026-110936 exposes OT engineering workstations to arbitrary code execution through DLL side-loading. Confirmed exploitation in the wild makes this a critical concern for organisations relying on Siemens engineering software.
Our latest OT Security Advisory covers:
🔹 Affected systems and the observed attack chain
🔹 Indicators of compromise and threat-hunting guidance
🔹 Recommended remediation and engineering workstation hardening measures
🔹 Additional OT vulnerabilities highlighted in recent CISA advisories
Key takeaway: Patching alone is not enough. Upgrade Siemens Software Center to version 4.0.9.8 or later, investigate potential compromise, and enforce execution controls to reduce exposure.
📄 Read the full advisory for actionable recommendations to strengthen your OT security posture.
#OTSecurity #CyberSecurity #IndustrialSecurity #ICS #SCADA #Siemens #VulnerabilityManagement #ThreatIntelligence